Compromised Official Reddit Account Used to Push HBO Max Malicious Ads in Rising ClickFix Cyber Threat Campaign

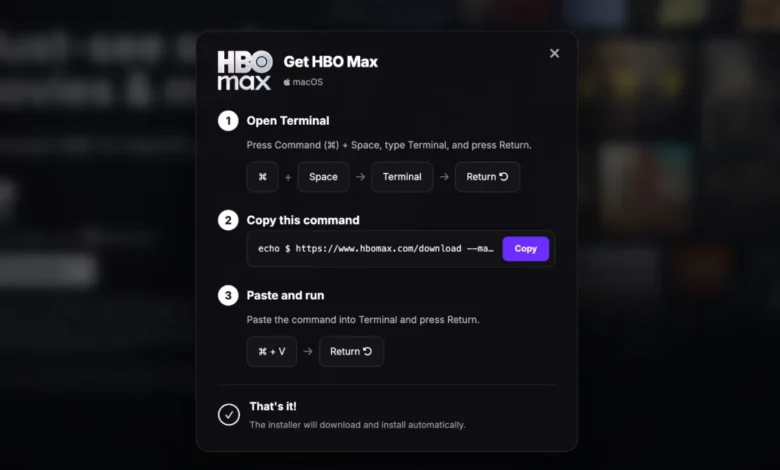
If you clicked on an HBO Max ad on Reddit over the past week, you might want to check your computer for malware. What initially appeared to be a standard promotional campaign on the popular social news aggregation and discussion platform has instead revealed itself as a sophisticated, weaponized distribution vector for malicious software. Security researchers have uncovered an aggressive cyberattack leveraging a compromised official Reddit account to broadcast hundreds of fraudulent advertisements. These ads directed unsuspecting users to deceptive landing pages, kicking off a rapidly growing digital threat methodology known throughout the cybersecurity industry as "ClickFix."
As digital adversaries continuously pivot toward psychological manipulation rather than traditional software vulnerabilities, ClickFix campaigns have swiftly ascended to become one of the most prominent and vexing cybersecurity threats of 2026. These attacks are growing increasingly stealthy, targeting consumer and enterprise devices with alarming frequency. Security analysts emphasize that the evolution of these campaigns marks a dangerous milestone in modern social engineering, transforming once-obscure internet tricks into an industrialized global enterprise designed to compromise thousands of personal and professional computers simultaneously.
Anatomy of a ClickFix Attack: How Users Trick Themselves
The mechanics of a ClickFix attack are deceptively simple yet devastatingly effective. The operation typically begins when a user visits a fraudulent website—or, in more alarming scenarios, a legitimate website that has been surreptitiously compromised by threat actors. Upon arrival, the visitor is greeted by a prompt designed to mimic benign, everyday web interactions, such as a traditional CAPTCHA challenge or an interactive anti-bot checkbox.
Once the user clicks the interface element, a fake error message or verification prompt materializes, claiming that an issue must be resolved before the user can proceed to the requested content. The prompt provides explicit instructions, urging the user to copy a specific string of text and paste it directly into their operating system’s native command-line interface—the Windows Command Prompt, PowerShell, or the macOS Terminal app.
The moment the user hits the enter key, they unwittingly and instantaneously execute a payload that installs advanced info-stealing malware onto their machine. This malicious software is engineered to immediately harvest sensitive data, including stored web browser passwords, session tokens granting access to logged-in accounts, financial credentials, and cryptocurrency wallets.
Because the execution vector relies on legitimate administrative tools native to the operating system, these attacks routinely bypass conventional antivirus programs and endpoint detection and response (EDR) defenses. By tricking the user into manually executing the code themselves, the hackers bypass perimeter security controls that would normally flag unauthorized executable files downloaded from the internet.
The Reddit Incident: A Compromised Corporate Presence
The severity of this threat vector was recently underscored by a high-profile security incident involving streaming giant HBO Max. According to threat intelligence researchers at Hudson Rock and discussions documented on Reddit’s dedicated cybersecurity community boards, malicious actors managed to infiltrate and take control of an official, verified corporate Reddit account belonging to HBO Max.
Once inside the account, the attackers wasted no time deploying their infrastructure. They utilized the trusted corporate handle to post hundreds of hyper-targeted, highly polished advertisements across various subreddits. These advertisements featured compelling branding designed to lure entertainment enthusiasts, but the underlying destination URLs directed traffic to sophisticated spoofed domains hosting ClickFix lures.
The deployment of ads from a verified corporate account granted the campaign an insidious veneer of legitimacy. Users browsing Reddit are accustomed to seeing sponsored content from major brands, and the presence of official account verification symbols heavily disarmed standard user skepticism. By weaponizing trusted corporate digital real estate, the threat actors successfully bridged the gap between institutional authority and malicious intent.
Chronology of the Campaign and Early Discovery
The unfolding of the HBO Max Reddit ad campaign highlights the rapid velocity at which modern cyberattacks are launched, detected, and analyzed within the global security community.
- Phase One: Compromise: Threat actors gain unauthorized access to the official HBO Max corporate account on Reddit, presumably through credential stuffing, session hijacking, or phishing targeting authorized marketing personnel.
- Phase Two: Deployment: Operating from the verified account, the attackers flood Reddit’s ad network with hundreds of fraudulent promotional posts over the course of several days, maximizing visibility across high-traffic communities.
- Phase Three: Lure and Hook: Victims interacting with the ads are redirected to external landing pages featuring convincing HBO Max branding accompanied by the trademark fake CAPTCHA or browser verification prompts.
- Phase Four: Execution: Users follow instructions to copy and paste obfuscated script payloads into their Windows Command Prompt or macOS Terminal, executing the info-stealing software.
- Phase Five: Discovery: Independent cybersecurity researchers at Hudson Rock identify the anomalous advertising pattern, cross-reference the compromised infrastructure, and publish initial warnings alongside community analysts on Reddit.
At the time of reporting, the full scope of the operational fallout remains unquantified. It is presently unclear precisely how many users interacted with the fraudulent advertisements or how many individual systems were successfully compromised before Reddit’s moderation and trust-and-safety teams intervened to pull the ads and lock down the compromised account. Warner Bros. Discovery, the parent company of HBO, and Reddit representatives did not respond to multiple requests for comment from journalistic outlets regarding the breach or their ongoing internal investigations.
The Evolution and Broader Context of ClickFix Operations
To understand the current wave of ClickFix operations, security analysts point to a distinct shift in attacker methodology. Until relatively recently, ClickFix attacks were isolated oddities. They typically capitalized on routine web searches where panicked users sought immediate technical fixes for minor software glitches, video playback errors, or missing DLL files. Attackers would position fake support forums or bogus driver update pages offering the same "copy-paste into terminal" remedy to resolve the faux error.
Over the past year, however, cybercrime syndicates have industrialized these tactics. Rather than waiting passively for victims to stumble across obscure forum posts, attackers are proactively injecting ClickFix lures into mainstream traffic channels—including compromised social media accounts, malvertising networks, and hijacked corporate web properties. This evolution represents a transition from opportunistic web trapping to aggressive, targeted digital ambushes.
Security experts note that the psychological success of ClickFix relies on a fundamental gap in digital literacy. While professional software developers and systems administrators routinely execute one-line snippets of code within command-line interfaces as part of their daily workflows, regular consumers almost never have a legitimate reason to open PowerShell, the Windows Command Prompt, or the macOS Terminal to browse the web or watch a video. However, when faced with an authoritative-looking error message styled to mimic system notifications or browser security checks, panicked or hurried users often suspend critical thinking and comply with instructions that appear technical and official.
Mitigation Strategies and Enterprise Defenses
Securing environments against human-centric execution vectors like ClickFix requires a multi-layered defensive strategy spanning individual user awareness, administrative lockdowns, and specialized endpoint security tools.
Enterprise environments face unique risks when employees browse social media or corporate networks on company-issued hardware. Prominent security researcher Kevin Beaumont highlighted that organizations managing fleets of Windows-based endpoints can significantly mitigate this threat by implementing centralized administrative policies. By blocking standard user access to the Command Prompt, PowerShell, and other administrative utilities across the entire domain, IT administrators can effectively neutralize the attack vector, ensuring that even if a user falls for the social engineering trick, the operating system will block the execution of the pasted payload.
For individual consumers and Mac users, specialized defensive software offers an additional layer of protection. Security guidance highlighted by technology publication Ars Technica points to utility tools such as BlockBlock, developed by Objective-See. BlockBlock is designed specifically to monitor persistence mechanisms and unauthorized script executions on macOS devices, alerting users whenever a process attempts to execute suspicious commands within the Terminal environment.
Implications for the Digital Advertising Ecosystem
The exploitation of Reddit’s advertising platform via a compromised corporate account casts a harsh spotlight on the systemic vulnerabilities inherent in modern digital advertising networks. As automated ad-buying systems and self-service promotional portals prioritize frictionless onboarding and rapid campaign deployment, vetting mechanisms for verified enterprise accounts occasionally lag behind sophisticated takeover techniques.
When threat actors can seamlessly hijack established corporate identities to distribute malware at scale, consumer trust in digital advertising is severely eroded. The incident forces both platform operators and enterprise brand managers to reevaluate the security postures surrounding their social media assets. Multi-factor authentication (MFA) enforcement, strict session management, and continuous anomaly detection on corporate marketing accounts are no longer optional best practices; they are critical frontline defenses preventing trusted brand names from being weaponized against their own audiences.
As the cybersecurity community continues to dissect the operational infrastructure behind the HBO Max Reddit campaign, users are strongly advised to exercise extreme caution when interacting with sponsored content, promotional links, or any web prompt requesting manual interaction with a computer’s command-line interface. In the landscape of modern cyber threats, if a website asks you to run code to prove you are human, the only thing you are proving is an invitation to compromise your own digital security.