WPBeginner Spotlight 29: WPVibe Passes 100,000 Users, OptinMonster MCP, and an Urgent PHP Fix

The month of October marked a monumental turning point for the WordPress ecosystem, officially transitioning artificial intelligence from a peripheral novelty into an integrated core utility. Across the content management system landscape, site administrators can now converse naturally with advanced language models like Claude and ChatGPT to orchestrate complex operations—ranging from programmatic popup construction to automated donation workflows and deep server diagnostics. However, alongside these unprecedented technological leaps, the month also brought critical security mandates, necessitating immediate administrative vigilance.
Critical Security Landscape: Emergency PHP and WordPress Patches
Before diving into the wave of automation innovations that defined the month, industry experts and security analysts emphasized a mandatory audit of server infrastructure. On October 21, core developers released emergency patches to neutralize two high-severity vulnerabilities discovered within the PHP programming language—the foundational architecture powering nearly half of all global websites. These critical security flaws carried the potential to allow unauthenticated remote attackers to execute arbitrary code directly on vulnerable hosting servers. Compounding the urgency, technical details regarding the vulnerabilities leaked publicly prior to official patch deployment, elevating the risk of active exploitation in the wild.
To mitigate these threats, hosting environments were urged to immediately upgrade to patched versions, specifically PHP 8.5.12, 8.4.27, 8.3.36, and 8.2.35. Sites running legacy iterations, such as PHP 8.1 or older, remained particularly exposed as they have officially exited their active security support windows. Industry associations stressed that standard WordPress core updates do not automatically update underlying server-level PHP configurations, requiring administrators to manually verify and adjust their software environments via hosting management panels or through the Site Health diagnostic tool within the WordPress dashboard.
Simultaneously, the WordPress core security team executed rapid maintenance cycles. October 6 saw the deployment of WordPress 7.1.3, addressing seven security vulnerabilities and four general maintenance bugs. This was followed closely on October 28 by WordPress 7.1.4, a targeted security release designed to patch several additional emerging vectors. Meanwhile, developers looking toward the horizon gained access to successive beta iterations of WordPress 7.2, with an official stable release slated for December 8, laying the groundwork for upcoming performance enhancements and block editor refinements.
The Rise of Conversational Administration: WPVibe Crosses 100,000 Users
Amidst the security updates, artificial intelligence integration achieved mainstream adoption, heavily anchored by the rapid ascent of WPVibe. Functioning as a free intermediary bridge, WPVibe seamlessly connects WordPress installations to prominent language models including ChatGPT, Claude, Cursor, and Grok, empowering users to execute administrative tasks using plain, conversational English rather than navigating deeply nested backend menus.
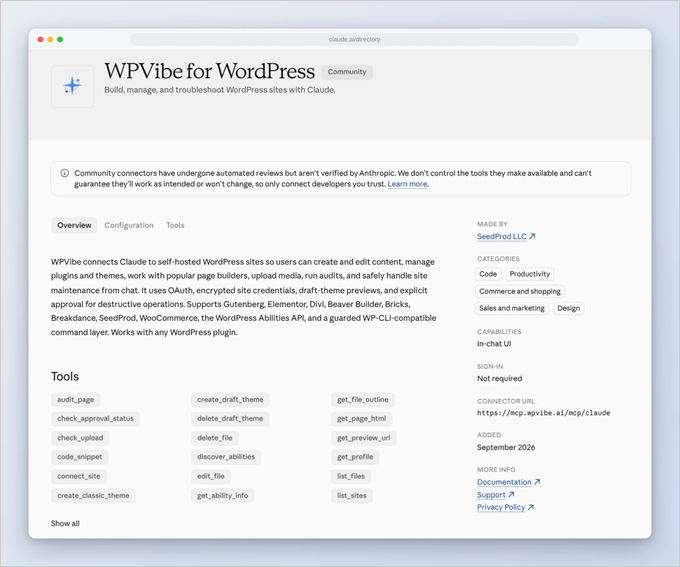
Data released by prominent figures in the ecosystem, including WPBeginner founder Syed Balkhi, confirmed that WPVibe crossed 100,000 active installations by the close of October—representing a staggering doubling of its user base from just 50,000 active installs at the end of September. This exponential growth was further accelerated when Anthropic officially incorporated WPVibe into Claude’s Connectors Directory. This integration eliminated the historical friction of manually configuring server endpoints, allowing administrators to establish secure AI connections directly from the Claude directory interface with a simple email authorization.
To cater to enterprise environments and high-volume administrators, WPVibe introduced version 1.20.0, featuring a specialized power-user toggle labeled "Dangerously bypass approvals." Designed strictly for staging environments or massive, automated batch jobs, the setting removes the default interactive prompts required for database modifications, deletions, and bulk edits. To maintain operational safety, the toggle remains disabled by default, requires explicit activation by a site administrator within the secure wp-admin portal, triggers persistent visual warning banners across administrative views, and maintains a comprehensive audit log of every automated instruction executed.
Furthermore, the plugin expanded its comprehension capabilities by launching 18 new native plugin integrations throughout October, cementing the paradigm that natural language processing is rapidly becoming a standard operational standard for everyday site management.
Conversion and Form Optimization: OptinMonster MCP and WPForms Updates
Conversion rate optimization tools also underwent a radical transformation driven by Model Context Protocol (MCP) standards. On October 27, OptinMonster unveiled the OptinMonster MCP—affectionately dubbed the "Monster Context Protocol." By treating language models as authorized virtual teammates, the protocol allows marketers to query traffic patterns, request data-driven campaign suggestions, and construct targeted popups, floating bars, or slide-ins entirely through conversational chat windows. This capability significantly reduces the analytical fatigue historically associated with parsing complex conversion metrics and historical reporting dashboards.
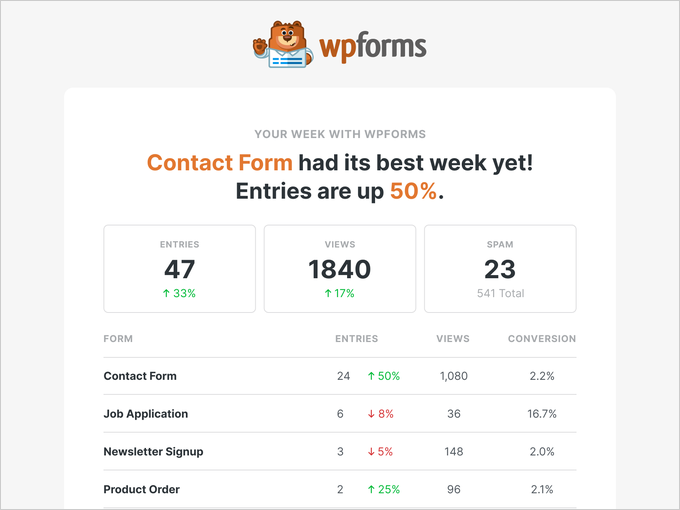
Complementing these AI-driven advancements, WPForms rolled out version 2.0.3 of its premier form-building software, used across more than 6 million active domains. The release featured a completely redesigned Weekly Email Summary. Shipped natively with all plans—including the free tier—the automated Monday dispatch provides concise reporting on weekly form activity, submission counts, view-through rates, and integrated spam analytics without requiring manual configuration.
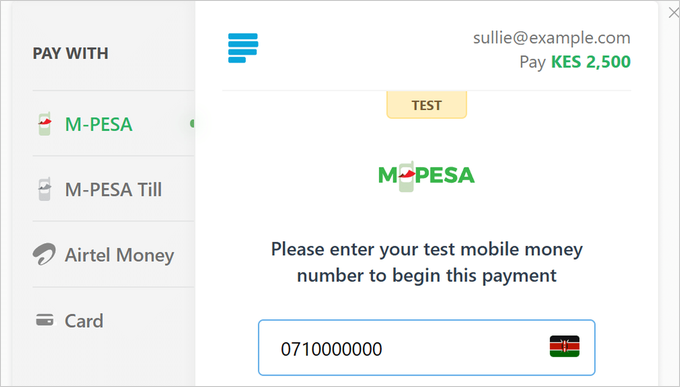
Addressing regional commerce needs, WPForms also introduced a dedicated Paystack addon. Designed to bridge the gap for digital merchants operating within African markets, the integration enables seamless transactions in local currencies across Nigeria, Ghana, South Africa, and Kenya. Customers can securely complete purchases using traditional payment cards, bank transfers, or regional mobile money solutions such as M-PESA and Airtel Money. To accommodate asynchronous settlement times inherent to bank transfers and mobile payments, WPForms introduced intelligent order-holding mechanisms, ensuring transactions remain in a pending state until financial clearance is fully verified by Paystack.
Workflow Automation and Infrastructure Management
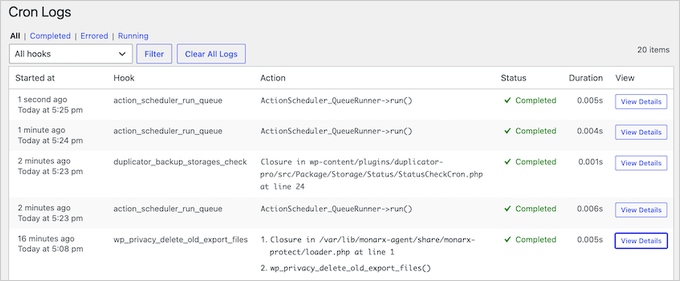
The broader plugin ecosystem experienced significant structural enhancements in October, highlighted by Duplicator’s acquisition and stewardship of WP Crontrol. Utilized across more than 300,000 websites, WP Crontrol serves as an essential utility for monitoring, debugging, and executing background scheduled tasks—commonly known as cron events—which handle automated backups, scheduled publishing, and transactional emails. Following a 14-year tenure under original creator John Blackbourn, the transition culminated in the release of WP Crontrol 2.0. The updated version democratized former Pro-tier features by integrating comprehensive cron event logging, failure tracking, and manual execution controls directly into the free core plugin.
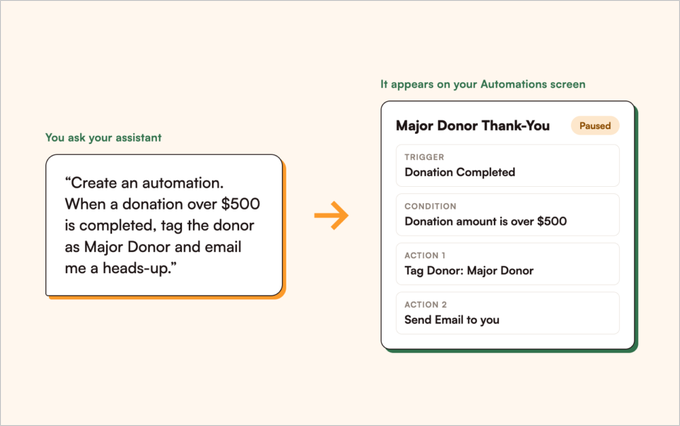
Concurrently, nonprofit fundraising platform Charitable introduced advanced automation capabilities via Automation Connect 2.4.0. Leveraging integration with WPVibe, fundraisers can now verbally instruct AI assistants to formulate intricate donation workflows—such as automatically tagging donors exceeding specific financial thresholds as major contributors and triggering administrative notifications—using a single sentence. Additionally, Charitable launched DonationExpress, an innovative full-screen mobile interface designed to bypass restrictive theme styling that often distorts or obscures donation buttons on mobile devices, alongside streamlined tools for merging duplicate donor profiles.
Email deliverability infrastructure similarly saw targeted upgrades. WP Mail SMTP released version 4.10, introducing redesigned analytical dashboards alongside free email deliverability reporting. The updated tooling provides granular tracking of total sent volumes, failure rates, open engagement metrics, and proactive connection diagnostics, allowing site administrators to verify communication pipelines before deployment errors impact critical user interactions such as password resets and e-commerce order receipts.
Finally, the All in One SEO team released Broken Link Checker 1.3.1, marking the plugin’s most comprehensive architectural expansion to date. Historically restricted to scanning standard posts, the updated scanner extends its algorithmic reach to evaluate navigation menus, author biographies, and custom database fields. Enhanced reporting dashboards now provide prioritized "Fix these first" recommendations, isolating critical dead links and ranking problematic external domains to preserve search engine optimization equity and protect user experience.
Broader Implications for the WordPress Ecosystem
The convergence of artificial intelligence protocols, heightened security protocols, and community-driven plugin acquisitions in October 2026 underscores a maturing digital publishing landscape. As core developers push toward future iterations like WordPress 7.2 while fortifying foundational server requirements, the barrier to sophisticated web management continues to lower. Routine administrative hurdles—from crafting marketing funnels and debugging server cron jobs to translating global content and managing complex donations—are increasingly mediated by conversational AI assistants operating securely within standardized protocol frameworks. For site owners, agencies, and developers alike, these developments signal an era where operational efficiency is matched only by an intensified focus on proactive server and software security hardening.
Related posts: