A Curated Collection of Essential WordPress Must-Use Plugins for Performance, Security, and Streamlined Administration

The proliferation of custom code repositories among long-term WordPress developers highlights a persistent workflow inefficiency within the content management system ecosystem. Developers frequently rely on recurring utility functions to optimize header outputs, deactivate unused native features, enhance security baselines, and eliminate interface friction for end users. Traditionally, tutorials have advised housing these scripts within a theme’s functions.php file. However, this method introduces vulnerability to data loss during theme transitions, child theme updates, or client-managed modifications. Consequently, industry standards have increasingly gravitated toward the must-use (mu-plugins) directory as a permanent, deployment-independent architectural home for essential site logic.
Understanding the Must-Use Plugin Architecture
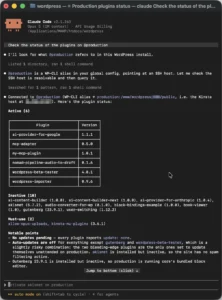
Must-use plugins, designated by the mu-plugins directory nomenclature, represent a specialized subset of WordPress extensions that execute automatically on every application request. Placed within the wp-content/mu-plugins/ folder, these standalone PHP files operate independently of the standard plugin activation workflow found in the WordPress administrative dashboard.
Historically rooted in the multi-site architecture of WordPress MU, the term "must-use" is somewhat misrepresentative, as these files function identically on single-site installations. When a request is initiated, WordPress loads all files residing in the mu-plugins repository prior to evaluating traditional plugins or theme components. Developers can monitor loaded must-use files directly through the administrative interface by navigating to Plugins followed by Must-Use, provided the script contains standard plugin header metadata. Without proper header comments, the files continue to execute normally but appear as unnamed entries within the administrative dashboard inventory.
The official WordPress Advanced Administration Handbook serves as the definitive technical reference for administrators managing these directories, detailing advanced configurations such as modifying default directory paths via the WPMU_PLUGIN_DIR constant.
Optimization and Performance Engineering
Site performance and resource efficiency frequently dictate the inclusion of lightweight, targeted utility scripts designed to eliminate redundant background processes. Modern web development paradigms emphasize the minimization of unnecessary data transmission and the reduction of browser-to-server overhead.
Removing Redundant Markup from the Document Header
Default WordPress installations inject numerous meta tags, discovery links, and version identifiers into the document head. These assets historically supported remote publishing clients, Windows Live Writer manifests, shortlinks, and oEmbed discovery protocols—features largely obsolete in contemporary web architecture. Furthermore, the inclusion of the core generator tag provides automated vulnerability scanners with explicit version intelligence. Implementing a clean-head routine strips these extraneous elements from every page load, reducing payload size and hardening system reconnaissance defenses. Developers must exercise caution when filtering feed links or REST API discovery endpoints, as specific third-party integrations may rely on these endpoints for proper functionality.
Mitigating Overhead Associated with Native Emoji Support
Introduced to ensure cross-browser compatibility for graphical emoticons, the native WordPress emoji script enqueues external JavaScript assets, stylesheet dependencies, and DNS prefetch routines targeting s.w.org on every page request. Given the universal support for native unicode emojis across contemporary web browsers, this functionality often represents unnecessary resource consumption. Comprehensive optimization routines disable emoji script injection across the classic editor, feed outputs, outgoing emails, and resource hints, thereby improving page load metrics and eliminating external DNS dependencies.
Eliminating Standalone Attachment Pages
Media uploads in WordPress automatically generate individual attachment pages designed solely to display the uploaded asset. On media-heavy web applications, search engine crawlers frequently categorize these sparse URLs as thin content, resulting in thousands of indexed pages with minimal informational value. Implementing an automated redirection rule ensures that any request directed at an attachment page triggers a permanent 301 redirect to the parent post or page, or alternatively to the domain root if no parent exists, thus preserving SEO equity and maintaining site architecture integrity.
Controlling Intermediate Image Size Generation
By default, WordPress generates multiple intermediate copies of every uploaded image to accommodate various theme and layout requirements. Across expansive media libraries, this behavior consumes substantial disk storage and increases backup archive volumes. Advanced administrators occasionally disable intermediate size generation entirely, preserving raw file uploads in their original dimensions. However, this approach requires alternative infrastructure, such as an external image content delivery network (CDN) or cloud offloading service, to prevent mobile visitors from downloading high-resolution assets that lack responsive srcset attributes.
Managing Post Revision Thresholds
Uncapped post revisions can exponentially expand the size of the wp_posts database table over time, introducing bloat that negatively impacts database query performance and backup durations. Implementing a strict numerical cap on stored revisions balances editorial flexibility with database optimization. Unlike static declarations within the wp-config.php file, dynamic filters enable administrators to establish conditional revision limits based on specific post types, enforcing stricter retention policies for standard pages while preserving comprehensive revision histories for core editorial content.
Privacy Compliance and Third-Party Request Reduction
Data privacy regulations, including the General Data Protection Regulation (GDPR), necessitate stringent control over outbound requests and data transmission to external third-party providers. Minimizing external dependencies not only enhances page rendering speeds but also reduces organizational compliance liability.
Neutralizing Native and Plugin-Level Artificial Intelligence Integrations
Recent iterations of the core platform introduced native artificial intelligence integration frameworks supported by specific global functions and conditional checks. Enterprise security policies, client non-disclosure agreements, and regional privacy frameworks frequently prohibit the automated transmission of content to third-party artificial intelligence models without explicit oversight. Deploying explicit filters across core systems, alongside popular third-party tools such as Jetpack and Elementor, prevents automated data routing and ensures organizational compliance prior to editorial deployment.
Disabling Gravatar Profile Avatars
Comment sections utilizing default avatar configurations initiate outbound HTTP requests to external Gravatar servers for every listed comment. Beyond introducing performance dependencies on third-party uptime, these requests transmit a cryptographic hash of the commenter’s email address, alongside visitor IP addresses and page context, to external infrastructure. Disabling avatar functionality entirely removes these external calls, streamlining page rendering and eliminating the necessity to document third-party data collection within site privacy policies.
Stripping External Requests from Administrative Dashboards
Popular search engine optimization extensions frequently inject administrative dashboard widgets that feature live external feeds. Rendering these components requires uncached HTTP requests sent to third-party servers upon every administrative dashboard load, transmitting core application version data as query parameters. Dequeuing associated stylesheets, scripts, and meta boxes isolates the administrative environment from external tracking and improves dashboard loading speeds.
Security Hardening and Core Infrastructure Management
Proactive security strategies require the systematic reduction of attack surfaces by disabling dormant functionalities, closing automated enumeration vectors, and ensuring timely patching schedules.
Automating Core Maintenance and Security Updates
While core background updates for minor and security releases are enabled by default, hosting environments or explicit configuration constants occasionally disable automated update protocols. Implementing dynamic filters guarantees that background maintenance patches are applied regardless of underlying configuration files, provided the server environment permits file write operations and lacks version control directories such as .git or .svn. Administrators must verify compatibility with host-level management policies to prevent conflicts with native patching schedules.
Counteracting User Enumeration Vectors
WordPress default behaviors expose valid administrative and editorial usernames across multiple public-facing endpoints, including user sitemaps, REST API user routes, author archive URLs, and explicit login error messages. Exposing valid usernames significantly reduces the complexity of brute-force authentication attacks. Comprehensive mitigation strategies involve disabling user sitemap providers, restricting REST API user endpoints for unauthenticated requests, redirecting author archives to 404 status pages prior to canonical redirection, and standardizing login error responses to provide ambiguous credential failure notices.
Deactivating Obsolete XML-RPC and Application Password Interfaces
Legacy protocols such as XML-RPC continue to serve as primary targets for distributed brute-force attacks and pingback amplification exploits. Disabling XML-RPC endpoints, pingback methods, and associated response headers neutralizes these attack vectors at the server gateway. Similarly, application passwords designed for external REST API authentication must be evaluated against organizational security policies; disabling unused authentication channels prevents potential credential misuse across unmonitored accounts.
Restricting File Modification and Administrative Editors
Built-in file editors within the WordPress administrative dashboard permit direct editing of theme and plugin PHP source code. In the event of an administrative account compromise, these interfaces provide immediate execution pathways for malicious actors to deploy persistent backdoors. Enforcing file modification restrictions via system constants or administrative permission filters ensures that live production code remains immutable from the browser interface.
Administrative Interface Customization and Environment Segregation
Optimizing the administrative experience for non-technical clients reduces operational friction and enhances perceived software quality. Concurrently, rigorous environment segregation practices ensure that staging and development instances cannot inadvertently impact production environments.
Hiding Non-Essential Administrative Notices
Plugin update prompts, promotional banners, and configuration wizards often clutter the administrative dashboard for client accounts. Restricting administrative notice visibility based on user capability thresholds ensures that editors and authors encounter a streamlined, professional workspace while maintaining critical system alerts for high-level administrators.
Enforcing Isolation on Staging and Demonstration Environments
Demonstration websites and staging clones require strict preventative controls to avoid accidental data leakage or operational disruption. Deploying short-circuit filters on outgoing mail functions prevents staging servers from transmitting automated transaction emails, password resets, or form notifications to external recipients. Similarly, disabling password reset routines on shared demonstration architectures prevents unauthorized users from altering shared administrative credentials, thereby maintaining system stability across collaborative review workflows.
Summary of Implementation Methodology
The consolidation of essential administrative utilities into must-use plugins establishes a resilient, portable, and performant foundation for WordPress site architecture. By decoupling custom utility code from theme dependencies, developers ensure long-term maintainability across iterative design updates. Centralized code repositories, such as community-managed GitHub collections, provide standardized access to these modular performance and security enhancements, facilitating rapid deployment across diverse client portfolios while adhering to enterprise development standards.
Related posts: